The California Privacy Rights Act (CPRA) is California’s 2020 ballot measure that amended the CCPA and expanded privacy rights that apply to covered employers handling California workforce data. The California Attorney General confirms that the employment-related data exemption expired on December 31, 2022, making current compliance processes essential for covered businesses.
This guide explains what the CPRA is, how it differs from the CCPA, which California employers are covered, and what practical controls support compliance – including sensitive personal information, consumer privacy request deadlines, vendor-contract requirements, enforcement exposure, and 2026 regulatory changes identified by the California Privacy Protection Agency.
Table of Contents
- Key Facts
- What is the California Privacy Rights Act (CPRA)?
- Does CPRA replace CCPA?
- What employee and consumer data does the CPRA protect?
- How did the CPRA change the CCPA?
- What rights do consumers and employees have under the CPRA?
- What CPRA compliance requirements apply to California employers?
- What are the CPRA enforcement risks and penalties?
- California Privacy Rights Act (CPRA) compliance tips
Key Facts
- The California Privacy Protection Agency confirms that the CPRA amends the CCPA, rather than replacing it, and its principal amendments took effect on January 1, 2023.
- For 2025, covered businesses include those with annual gross revenue of at least $26.625 million, those handling personal information of 100,000 or more California residents or households, or those deriving 50% or more of annual revenue from selling or sharing personal information, according to the California Privacy Protection Agency.
- In March 2025, the California Privacy Protection Agency ordered a $632,500 privacy enforcement fine and required process changes, showing that poor request handling and vendor controls can create material exposure.

What is the California Privacy Rights Act (CPRA)?
There is no all-encompassing US federal employment law relating to employee data protection in the United States. Instead, there is a vast range of data privacy and data security laws that have been enacted on both the federal and state levels which serve to protect the personal data of U.S. employees and consumers. One such example is the California Privacy Rights Act (CPRA).
So, what is CPRA?
California is known for its progressive laws, especially those enacted in more recent years. Examples of these trailblazing laws include the California Pay Transparency Law and the California Family Rights Act (CFRA) which protects an employee’s right to take bereavement leave, amongst other provisions. The CPRA is another example of how the State of California is leading the way in terms of consumer and workplace protections.
The California Privacy Rights Act (CPRA) is a US data privacy law targeted at businesses based or operating in the state of California. It was adopted via referendum and went into effect on January 1, 2023. At its core, it aims to protect data privacy rights, including those of employees and consumers. It also expands on existing privacy data laws (namely, the CCPA which was enacted in 2018) and defines how businesses must operate when they collect, store, use, and share employee and consumer data.
Specifically, under the CPRA, the citizens of California have gained a number of new rights, including the right to:
- Correct personal information
- Prevent the use of sensitive personal information
- Opt out of personal information being shared with third parties
As the first comprehensive consumer privacy legislation of its kind in the U.S., the CPRA is changing the way companies do business and serves as a potential model for other states looking to improve their data privacy laws.
Does CPRA replace CCPA?
Many people confuse the California Consumer Privacy Act (CCPA) with the California Privacy Rights Act (CPRA). However, they are not the same thing.
CPRA vs CCPA: What’s the difference?
The California Consumer Privacy Act (CCPA) is a law that was initially approved in 2018 and went into effect in 2020. This law regulates how businesses collect, store, share, and sell consumers’ personal information and data.
The California Privacy Rights Act (CPRA), approved by California voters in 2020, amended the existing CCPA. The California Privacy Protection Agency confirms that the CPRA amendments took effect on January 1, 2023, and the law is generally referred to as the CCPA, as amended.
Let’s take a look at some of the key differences between CPRA vs. CCPA to help you understand the difference.
| Topic | CCPA baseline | CPRA expansion |
|---|---|---|
| Privacy choices | Know, delete, and opt out of sale | Adds correction, limits on sensitive personal information, and opt-out of sharing |
| Workforce data | Employment-data exemption applied temporarily | Exemption expired on December 31, 2022 |
| Enforcement | Attorney General enforcement | CPPA administrative enforcement and audits |
The California Privacy Protection Agency confirms these current distinctions between the CCPA framework and CPRA amendments.

The California Consumer Privacy Act (CCPA) was signed into law in 2018 and went into effect on January 1, 2020. It established a range of business obligations and consumer privacy rights relating to the collection and sale of personal data.
This included a consumer’s right to:
- Opt out of the sale of their personal data
- Delete personal information collected about and from them
- Nondiscrimination for exercising their CCPA rights
The California Privacy Rights Act (CPRA), also known as Proposition 24, doesn’t replace the CCPA. Instead, it significantly amends and expands the existing provisions of the CCPA.
This includes the right to:
- Opt-out of cross-contextual advertising.
- Contractual commitments from service providers relating to the protection and use of personal data. This includes how long a business can retain each category of personal data, which should be explained in a company’s public consumer privacy notice.
- The protection of employment data, not just consumer data.
The CPRA also expands the definition of breach liability. As a result, liability now also takes into account unauthorized access or disclosure of certain data elements (email addresses, passwords, security questions, etc.). Plus, it has added new provisions related to the establishment of a new government agency for the enforcement of data privacy laws in California, known as the California Privacy Protection Agency.
Related: California Employment Law explained
What employee and consumer data does the CPRA protect?
If you are an employer or small business owner based in or operating within California, you must understand which data the California Privacy Rights Act (CPRA) protects. Essentially, the CPRA covers any personal data that could identify an employee or a consumer.
This includes, but isn’t limited to:
- Names
- Email addresses
- Phone numbers
- The contents of phone calls, emails, and text messages
- Social Security Numbers (SSN)
- Physical addresses
- Driver’s license numbers
- State identification cards
- Passport numbers
- Account login information
- Bank account numbers
- Debit and credit card numbers
- Any data related to geolocation, racial or ethnic origin, religious or philosophical beliefs, union membership, or genetic and biometric information
- Any other personally identifiable information
The CPRA does not classify information that is publicly available from governmental records as personal information.
How did the CPRA change the CCPA?
Let’s take a look now at some of the changes and expansions under the California Privacy Rights Act (CPRA).
There are 6 main differences between the CCPA and the CPRA that you need to be aware of.
These relate to:
- The criteria for qualifying as a business
- Modified consumer privacy rights
- A new category of protected data
- The adoption of GDPR principles
- The expansion of the private right of action
- The creation of a new privacy enforcement authority
Let’s take a look at these points in a bit more detail.
Criteria for qualifying as a business
An important change relates to the criteria for qualifying as a business.
Let’s look first at what the guidelines were under the CCPA (changes in bold).
According to the CCPA, data privacy provisions applied to all for-profit businesses that met one or more of the following thresholds:
- Has an annual gross revenue of over $25 million
- Makes 50% or more of its annual revenue from selling personal data
- Buys, sells, or receives the personal data of 50,000 or more California residents for commercial purposes, alone or jointly.
The CPRA has expanded these guidelines. The law now applies to for-profit legal entities that meet one or more of the following thresholds:
- Has an annual gross revenue of at least $26.625 million, the inflation-adjusted figure published by the California Privacy Protection Agency for 2025
- Makes 50% or more of its annual revenue from selling or sharing personal data
- Buys, sells, receives, or shares the personal information of 100,000 or more households or consumers annually, alone or jointly
5 modified consumer privacy rights
The CPRA has also modified and expanded the definition of consumer privacy rights.
Previously, the CCPA created 5 specific rights for consumers.
This included the right to:
- Know what personal information is collected, used, and shared with third parties, including where it was collected from, why it was collected, and, if sold, to whom.
- Delete any collected personal data.
- Opt-out of the sale of personal data (if applicable).
- Non-discriminatory treatment for exercising any rights.
- Initiate a private cause of action for data breaches.
The CPRA has included 2 additional consumer privacy rights:
- Firstly, the right to correct inaccurate personal information.
- Secondly, the right to limit the disclosure and use of sensitive personal information. This includes stopping their data from being collected and shared along a complex targeted advertising ecosystem (e.g., automated decision-making technology, including profiling).
New category of protected data: SPI
Another important change relates to the definition of personal data.
The CPRA distinguishes sensitive personal information (SPI) from broader personal information. The California Privacy Protection Agency explains that SPI includes specified government identifiers, account credentials, precise geolocation, genetic data, certain biometric data, health information, and information about race, ethnicity, union membership, or sexual orientation.
As we mentioned above, according to the CPRA, sensitive personal information includes:
- Government identifiers, including Social Security, driver’s license, state identification card, and passport numbers
- Account login credentials and financial account, debit card, or credit card information when paired with access credentials
- Precise geolocation, genetic data, and biometric information used to identify a person
- Information concerning health, sex life, sexual orientation, racial or ethnic origin, citizenship or immigration status, religious beliefs, or union membership
Essentially, if you collect any of this data from your workforce (which you undoubtedly do), then your employees have the right, under the CPRA, to receive notice of said collection. Moreover, they also have the right to be notified if you sell or share any of this sensitive data. California-resident employees may have rights to know, delete, correct, and, where applicable, limit the use or disclosure of SPI or opt out of sale or sharing.
3 GDPR Principles adopted
Many businesses note similarities between the CPRA and Europe’s General Data Protection Regulation (GDPR), particularly around data minimization, purpose limitation, and retention controls. However, the CPRA is a California privacy law, not an adoption of the GDPR. The California Privacy Protection Agency confirms that covered businesses must limit collection, use, retention, and sharing to purposes that are reasonably necessary and proportionate.
These GDPR principles, guided by the concept of lawfulness, fairness, and transparency, relate to:
- Data minimization: Companies are required to limit the collection of personal data that is deemed directly necessary and relevant to the nature of the business.
- Storage limitation: Businesses are only permitted to retain and store personal data for a reasonable amount of time.
- Purpose limitation: Businesses can only collect personal data for explicit, specific, and legitimate disclosed purposes.
This makes it much easier to ensure compliance with both laws if your business is operating in both US and European territories.
Moreover, much like the GDPR, the CPRA also establishes a specific governing body for regulating the provisions of the Act. This body is known as the California Privacy Protection Agency (CPPA), and it has full administrative power, authority, and jurisdiction to implement and enforce the CPRA.
Expanded private right of action
A further important change relates to a consumer’s private right of action.
But, what does this mean?
Basically, the California Privacy Rights Act (CPRA) has expanded the CCPA’s scope for the private right of action. The private right of action is limited. The California Attorney General explains that an individual may sue only for certain data breaches involving nonencrypted and nonredacted personal information when the breach resulted from a business’s failure to maintain reasonable security procedures and practices. Previously, the CCPA included provisions for the private right of action. However, the CPRA has expanded these provisions so that they now also include additional types of personal information. These additional types of personal information include email addresses, security questions and answers, and passwords.
New privacy enforcement authority: CPPA
Finally, as we mentioned above, the California Privacy Rights Act (CPRA) includes the establishment of an official governing body. This governing body is known as the California Privacy Protection Agency (CPPA) and it is directly responsible for regulating the Act. It has the authority to investigate claims of data privacy breaches and enforce corrective actions, including the assignment of non-compliance penalties. Moreover, the CPPA is also responsible for promoting awareness of the CPRA and has the power to issue further regulations where applicable.
Previously, the CCPA was enforced by the California Office of the Attorney General (OAG). Instead, a specific governing body is now exclusively responsible for enforcing the protection of sensitive personal information. This should hopefully result in higher levels of data privacy compliance in the state.
What rights do consumers and employees have under the CPRA?
Under the terms of the California Privacy Rights Act (CPRA), your employees and customers have the right to:
- Be informed of the data you are collecting and their corresponding rights.
- Request that you disclose what sensitive personal information you have collected, and what the specific purpose of collecting this data is.
- Correct any sensitive personal information that you hold.
- Limit how you use their sensitive personal information unless it is necessary for you to perform the services or provide the goods they are requesting.
- Opt out of third-party data sales.
- Take legal action if you expose their non-encrypted sensitive personal information.
- Receive heightened protection where a business has actual knowledge that a consumer is under 16. The California Privacy Protection Agency states that certain violations involving minors can carry higher administrative fines.
What CPRA compliance requirements apply to California employers?
As an employer or business owner, if you qualify under the provisions of the California Privacy Rights Act (CPRA), you have a number of specific obligations.
In particular, these obligations mean you have to:
- Provide a notice at collection at or before collecting personal information. California Legislative Information states that the notice must identify the categories collected, the purposes for collection or use, whether information is sold or shared, and the retention period or criteria used to determine it.
- Honor these consumer rights.
- Fulfill all your obligations relating to the disclosure and retention of sensitive personal information.
- Facilitate consumer requests relating to the omission, retraction, or sharing of sensitive personal information unless you specifically require access to this information in order to provide the products or services that a consumer has requested.
- Facilitate requests relating to the disclosure and amendment of sensitive personal information.
- Maintain written contracts with service providers, contractors, and third parties that limit permitted uses of personal information, require equivalent privacy protection, require notice when obligations cannot be met, and allow the business to stop and remediate unauthorized use. California Legislative Information sets out these contract requirements in Civil Code § 1798.100.
- Implement security safeguards, such as the encryption of sensitive personal information.
What changed for covered businesses in 2026?
Updated CCPA regulations became effective on January 1, 2026. The California Privacy Protection Agency states that certain covered businesses now face phased requirements concerning cybersecurity audits, privacy risk assessments, and automated decision-making technology, with some compliance deadlines beginning in 2027 and 2028.
What are the CPRA enforcement risks and penalties?
So, what happens if you don’t comply with the CPRA?
In the event of non-compliance with any of the obligations established by the California Privacy Rights Act (CPRA), the California Privacy Protection Agency (CPPA) has the right to impose a number of penalties.
What are these penalties?
Basically, these include:
- Administrative fines of up to $2,663 per violation, or up to $7,988 per intentional violation and certain violations involving consumers under 16. The California Privacy Protection Agency adjusted these amounts effective January 1, 2025.
- Statutory damages for qualifying data breaches of not less than $107 and not more than $799 per consumer per incident, or actual damages if greater. The California Privacy Protection Agency adjusted this range effective January 1, 2025.
- Non-monetary relief. If an employee or consumer files a claim for a security breach violation, they are also entitled to seek injunctive or declaratory relief, as well as any other relief the court deems appropriate.
Unquestionably, the best way to avoid these penalties is to implement standards and procedures that ensure you handle all consumer and employee data in a responsible and ethical manner. For example, you should develop stronger data protection processes and controls and adapt to any new data privacy compliance requirements that might be included in the Act in the future.
California Privacy Rights Act (CPRA) compliance tips
Above all, there are two main aspects you need to consider and evaluate to ensure CPRA compliance:
- What changes do you need to make to your internal processes, policies, procedures, and systems to ensure ongoing compliance?
- How will you notify your customers, partners, and employees of the changes and their additional rights under the CPRA?
Here are a few additional tips to help you with this:
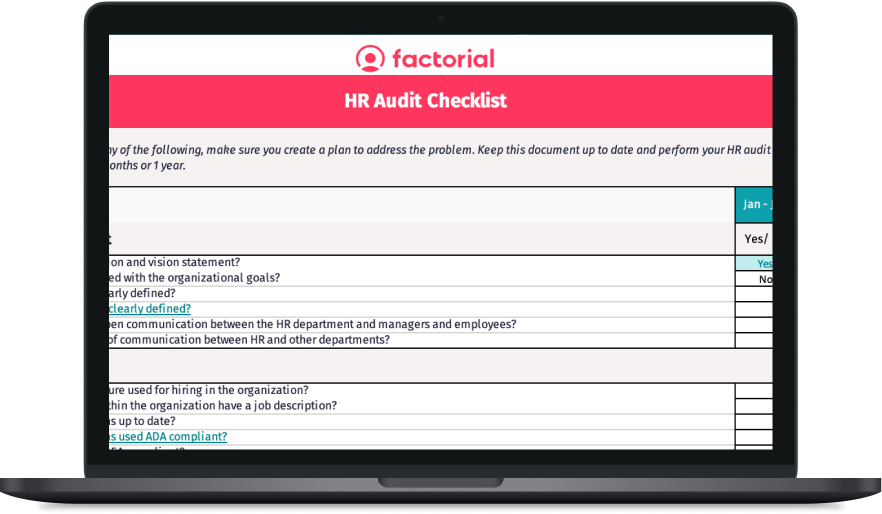
- The first step is conducting a detailed audit of the data your organization collects. Above all, make sure you understand the types of data you collect, why you collect it, how you handle it, and how you protect it. You should also identify which categories of data are sensitive personal information and consider removing the collection of any data that is not strictly necessary for the purpose of your business.
- Secondly, make sure your employees and customers are aware of their rights under this law.
- Thirdly, review and update your internal processes, policies, procedures, and systems so that they comply with all requirements of the CPRA.
- Additionally, update your privacy notice so that it aligns with CPRA disclosure requirements.
- Likewise, it’s also a good idea to update your contracts with employees, service providers, contractors, and third parties to ensure they include the required CPRA provisions.
- Moreover, conduct a comprehensive privacy and cybersecurity risk assessment.
- Lastly, use an encrypted document management system to handle all the SPD that you collect, store, and manage.
Use a documented data inventory to assign an owner, legal purpose, retention rule, access group, and vendor recipient to each category of workforce data. Factorial, all-in-one business management software, can help teams keep employee records and compliance documents organized while maintaining a clear audit trail for internal reviews.
Operational checklist:
- Confirm whether the business meets a CCPA applicability threshold.
- Map employee, applicant, contractor, and emergency-contact data flows.
- Publish or update workforce notices at collection.
- Configure a documented process for access, deletion, correction, opt-out, and SPI-limit requests.
- Review vendor contracts and retain evidence of privacy controls, decisions, and request responses.
Ultimately, by understanding all your obligations under the California Privacy Rights Act (CPRA) and designing a comprehensive plan of action to ensure compliance, you can successfully avoid undesirable enforcement penalties. Above all, this is important because non-compliance can not only damage your company’s finances – it can also have a negative effect on your brand and reputation.
Important: CPRA compliance is fact-specific. Employers should obtain qualified legal advice when determining whether an exemption applies, responding to a complex verified request, assessing a vendor relationship, or implementing automated decision-making tools in employment processes.
FAQ
Do I have to comply with CCPA?
You must comply with the CCPA, as amended by the CPRA, if your for-profit business meets one of the following: has annual gross revenue over $25 million, derives 50% or more of its annual revenue from selling or sharing personal data, or buys, sells, or shares the personal information of 100,000 or more consumers.
What is a CPRA compliance checklist?
A CPRA compliance checklist outlines key actions for businesses, such as auditing the data you collect, updating privacy notices and internal policies, and informing individuals of their rights. It also includes implementing security safeguards, like using an encrypted document management system, to protect sensitive personal information.
Who is covered under CPRA?
The CPRA protects the personal data of California employees and consumers. This includes any information that could identify an individual, such as names, email addresses, Social Security numbers, and geolocation data, as well as other sensitive personal information collected and stored by a business.